

Cybersecurity Consulting
Board-level advisory and virtual CISO leadership that turns security from a cost centre into a competitive edge — with architecture reviews and resilience planning built around how your business actually runs.
We help organisations identify risks, strengthen defenses, and achieve compliance through expert-led VAPT, GRC and cybersecurity advisory services.
Industry-Recognised Experts
Certified security consultants with real-world experience.
Proven Methodology
Structured, standards-based and industry-aligned approach.
Actionable Insights
Clear recommendations your business can act on.
Business-Focused
Security strategies aligned with your goals.
At Aesparrow Consulting Pvt. Ltd., we are committed to delivering innovative, tailored, and resilient cybersecurity solutions that protect organizations from today’s rapidly evolving digital threats. Founded by industry experts, Aesparrow’s mission is to secure your business with the highest standards of security practices — from infrastructure protection and compliance to cyber risk management.
We understand that cybersecurity is more than just defense — it’s about strategically managing risk, ensuring regulatory compliance, and empowering growth in a secure environment. Whether you’re a startup or a global enterprise, Aesparrow offers customized cybersecurity solutions aligned with your unique business objectives.
Advisory, Testing, Compliance, and Response.
Board-level advisory and virtual CISO leadership that turns security from a cost centre into a competitive edge — with architecture reviews and resilience planning built around how your business actually runs.
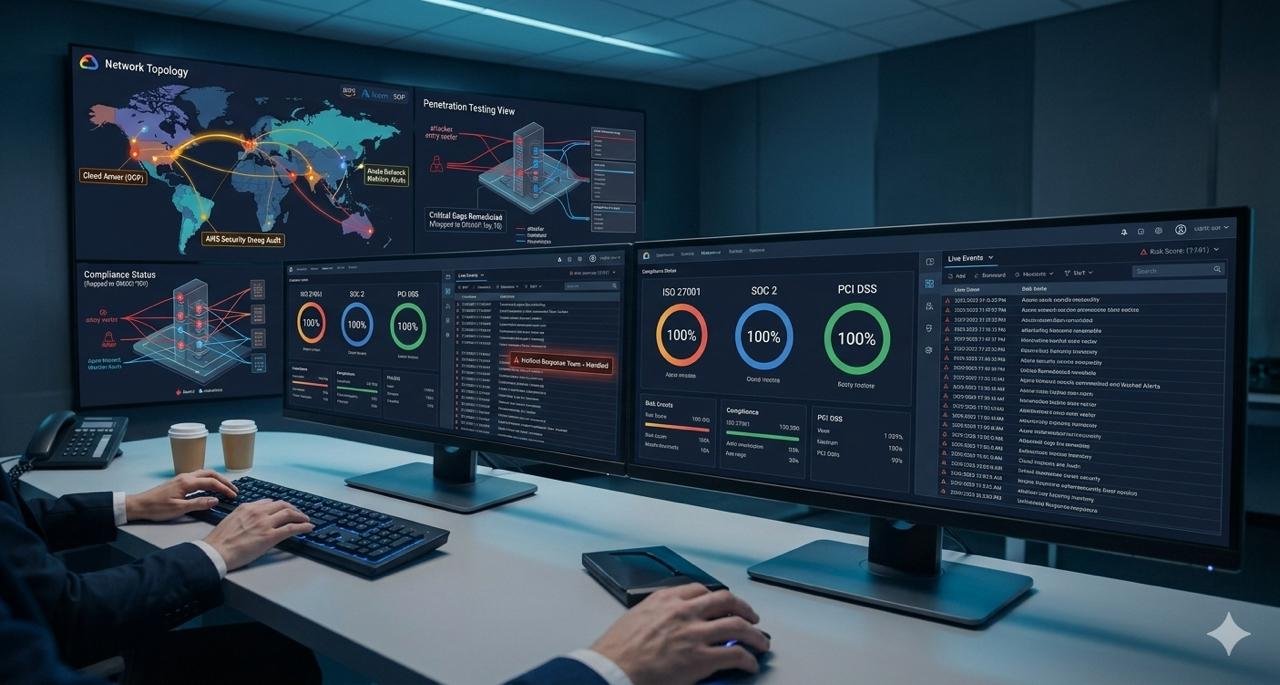
We Guard What You Build — Security That Never Sleeps.
Explore our servicesGreat security shouldn't slow you down. We work alongside your engineers and leaders to find the gaps that matter, fix them at the root, and build the habits that keep them closed — mapped to OWASP, NIST, and ISO 27001 so the results hold up to any auditor or customer questionnaire.
See your systems the way an attacker does — and fix what matters first.
ISO 27001, SOC 2, and PCI DSS readiness, minus the busywork.
Round-the-clock monitoring and a response team on standby.
Harden AWS, Azure, and GCP against misconfiguration and exposure.
Comprehensive security testing services to identify risks, strengthen your defenses, and ensure your business stays ahead of cyber threats.
Identifies vulnerabilities in web applications, such as injection flaws, broken authentication, and cross-site scripting (XSS), based on OWASP Top 10. Ensures secure development and deployment of your web platforms.
750+
Global Clients
50+
Team Members
200+
Projects Delivered
10+
Frameworks Covered
Certified, practising security professionals on every engagement, with senior review of every report.
Structured, repeatable testing and audit methodology refined across hundreds of engagements.
Prioritised, developer-ready findings with business impact analysis — not noise.
Every engagement scoped to your industry, scale, and threat model.
Free re-testing of fixes and continued advisory after every engagement.
We translate technical risk into decisions your board understands.
Latest Threats & Trends
Threat actors are actively attempting to exploit a now-patched security flaw in Veeam Backup & Replication to deploy Akira and Fog ransomware.
Thought Leadership
The Iranian threat actor known as OilRig has been observed exploiting a now-patched privilege escalation flaw in the Windows kernel in an espionage campaign targeting the UAE and the wider Gulf region.
Tools & How-To Guides
Cybersecurity researchers have found that entry points could be abused across multiple programming ecosystems like PyPI, npm, Ruby Gems, NuGet.
From vulnerability assessment and penetration testing (VAPT) to ISO 27001 implementation, SOC 2 readiness, cybersecurity audits, and Governance, Risk & Compliance (GRC), Aesparrow helps organizations identify security gaps, strengthen controls, and prepare for evolving compliance requirements. Explore our services to find the right expertise for your security and risk management goals.
As cyber threats evolve and security requirements grow, organizations must do more than protect their systems. They need to identify vulnerabilities, validate security controls, manage risks, and demonstrate compliance. Proactive security testing and a strong compliance strategy help businesses strengthen resilience, protect sensitive data, and build lasting trust.
Security testing and compliance programmes tailored to your sector’s threats and regulations.
Tell us what you need tested for a fixed-scope quote, or talk it through with an Aesparrow practitioner — no obligation, no sales script.


